As connected medical instruments, laboratory systems, and industrial devices continue to evolve, cybersecurity is no longer an afterthought. The European Union’s Cyber Resilience Act (CRA) is accelerating a shift toward security-by-design, requiring manufacturers of connected products to consider cybersecurity across the entire product lifecycle, from development and deployment through vulnerability management and updates.1,2
Many of Novanta Precision Medicine’s products operate at the digital edge where critical data is captured, authenticated, displayed, or communicated to higher-level systems. In that role, our technologies can help OEMs build devices and workflows that support broader cybersecurity and data integrity objectives in response to the growing cybersecurity regulatory landscape. 1
For OEM engineers developing next-generation medical, life science, and industrial systems, the question is increasingly becoming:
How do we ensure that the data entering our connected device ecosystem is trustworthy, traceable, and secure from the start?
Understanding the CRA’s Impact on OEMs
The CRA establishes cybersecurity requirements for products with digital elements sold within the European Union. Manufacturers must implement cybersecurity throughout the design, development, deployment, and maintenance phases of their products while maintaining processes for vulnerability management and security updates.1,2
For many medical and industrial OEMs, compliance extends beyond software. Device manufacturers must evaluate how data enters their systems, how users are authenticated, how assets are tracked, and how information moves between subsystems. These considerations make the technologies that sit closest to the user, specimen, consumable, or operator increasingly important.
CRA Enablement Begins at the Digital Edge
Connected devices are only as trustworthy as the data they receive. Whether your system is identifying a reagent, authenticating a consumable, tracking a medical asset, or displaying critical information to an operator, cybersecurity starts before data reaches the cloud or enterprise software platform.
This is where Novanta’s technologies can help.
RFID Technologies for Identity, Authentication, and Traceability
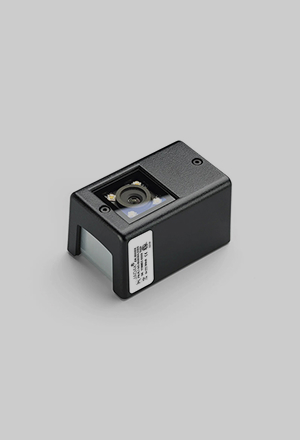
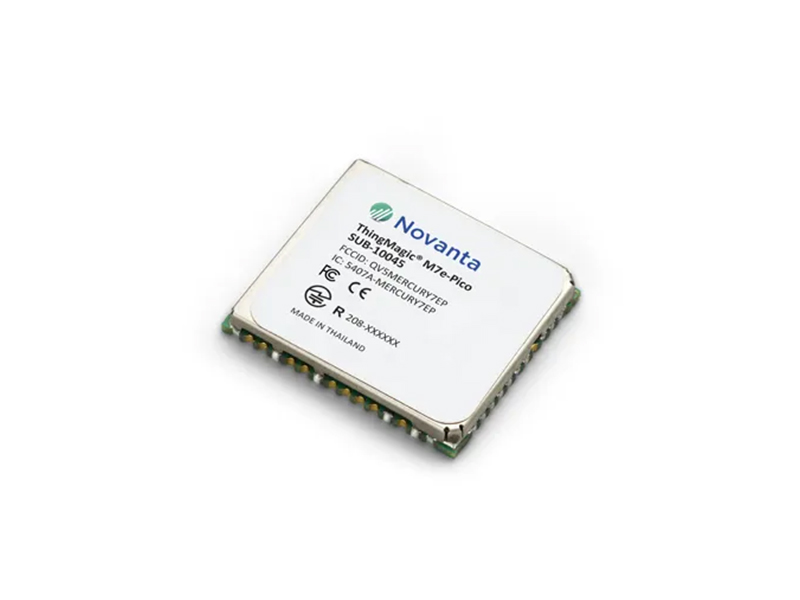
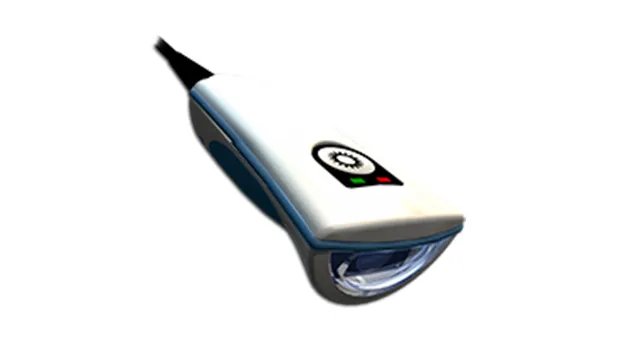
ThingMagic® RFID Solutions provide OEMs with embedded RFID modules, readers, development tools, and RFID-enabled hand scanners designed for applications including laboratory automation, medication management, hospital asset tracking, and consumable authentication. These solutions offer protocol flexibility, cryptographic security capabilities, and integration support for OEM development programs.
In a CRA-focused environment, RFID technologies can:
- Improve asset and consumable traceability
- Authenticate components and reagents
- Reduce manual data-entry risks
- Support chain-of-custody workflows
- Enable secure identification and tracking architectures
These capabilities become increasingly valuable when demonstrating how devices protect the integrity of operational and clinical data. 3
Embedded Displays That Support Secure Workflows
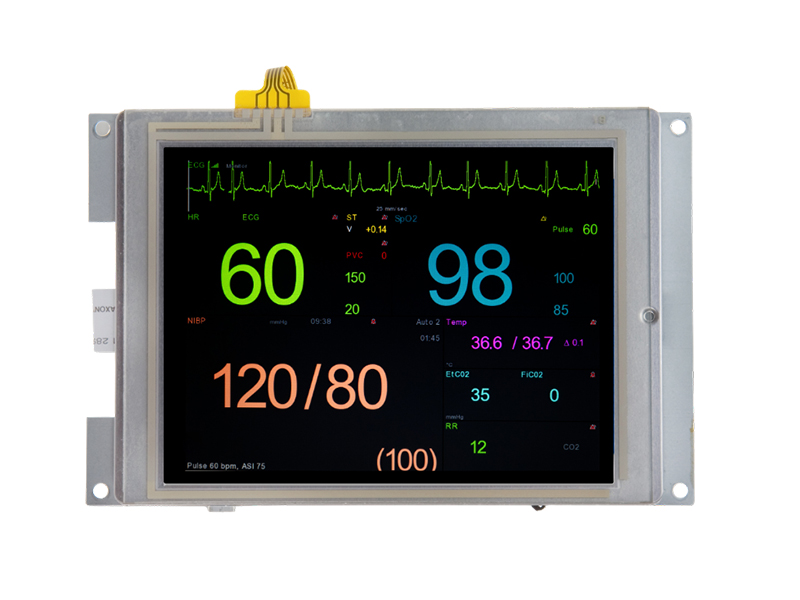
Novanta’s Embedded Displays provide the operator interface for many OEM systems. Human-machine interfaces are often where users authenticate, configure devices, acknowledge alarms, and review system status.
A well-designed embedded display platform can support:
- Controlled user interactions
- Clear presentation of critical information
- Workflow validation
- System configuration and diagnostics
- Integration with secure application architectures
As cybersecurity regulations increasingly emphasize security-by-design principles, thoughtful HMI design becomes an important component of the overall product security strategy.4
Connected Healthcare and Intelligent Devices
The healthcare industry is increasingly adopting connected technologies that gather real-time operational and patient-related information. Recent collaborations around RFID-enabled healthcare workflows demonstrate how connected devices can support medication management, monitoring, traceability, and operational efficiency while improving patient safety. 3,5
For OEMs developing connected instruments, diagnostics systems, wearable technologies, and smart medical devices, the integrity of collected data is just as important as the security controls protecting it.
Engineering Partnership Matters
Cybersecurity requirements are becoming too complex for component selection alone to solve.
Many OEMs need engineering support to determine:
- Which identification technologies best fit their architecture
- How to implement secure traceability workflows
- How to integrate RFID into medical or industrial systems
- How to design operator interfaces that support secure workflows
- How edge devices can contribute to broader cybersecurity objectives
At Novanta, our engineers work directly with OEM engineering teams to help accelerate development and integration efforts. From embedded RFID to touchscreen displays and complete subsystem design support, we collaborate engineer-to-engineer to help customers build robust solutions for demanding applications.
Looking Beyond Compliance
The CRA is driving an important industry conversation: cybersecurity must be built into connected systems from the beginning rather than added later. 1,2
While not every component supplier is responsible for CRA requirements, every technology provider has a role in helping OEMs create systems that are more secure, more traceable, and more resilient.
For organizations developing the next generation of connected medical and industrial devices, trusted data capture, secure identification, and reliable operator interaction are all foundational elements of a successful cybersecurity strategy.
Learn More
Looking for ways to support the deployment of your secure device?
- Explore our OEM Medical Solutions Guide
- Learn more about our ThingMagic RFID Solutions
- Discover our Embedded Displays
- Contact our technical experts to discuss your application and integration requirements
When cybersecurity starts at the edge, better architecture decisions happen from day one. Let’s build them together.
1https://digital-strategy.ec.europa.eu/en/policies/cyber-resilience-act
2https://digital-strategy.ec.europa.eu/en/policies/cra-manufacturers
4 https://digital-strategy.ec.europa.eu/en/policies/cra-manufacturers
5 https://www.rfidjournal.com/news/identiv-novanta-announce-partnership-for-healthcare-rfid/223024/